External Attack Surface
Your own attack surface
Unknown IT assets, publicly reachable services, misconfigurations and undetected vulnerabilities can open up new opportunities for attackers.
Do you know what attackers can see of your organization?
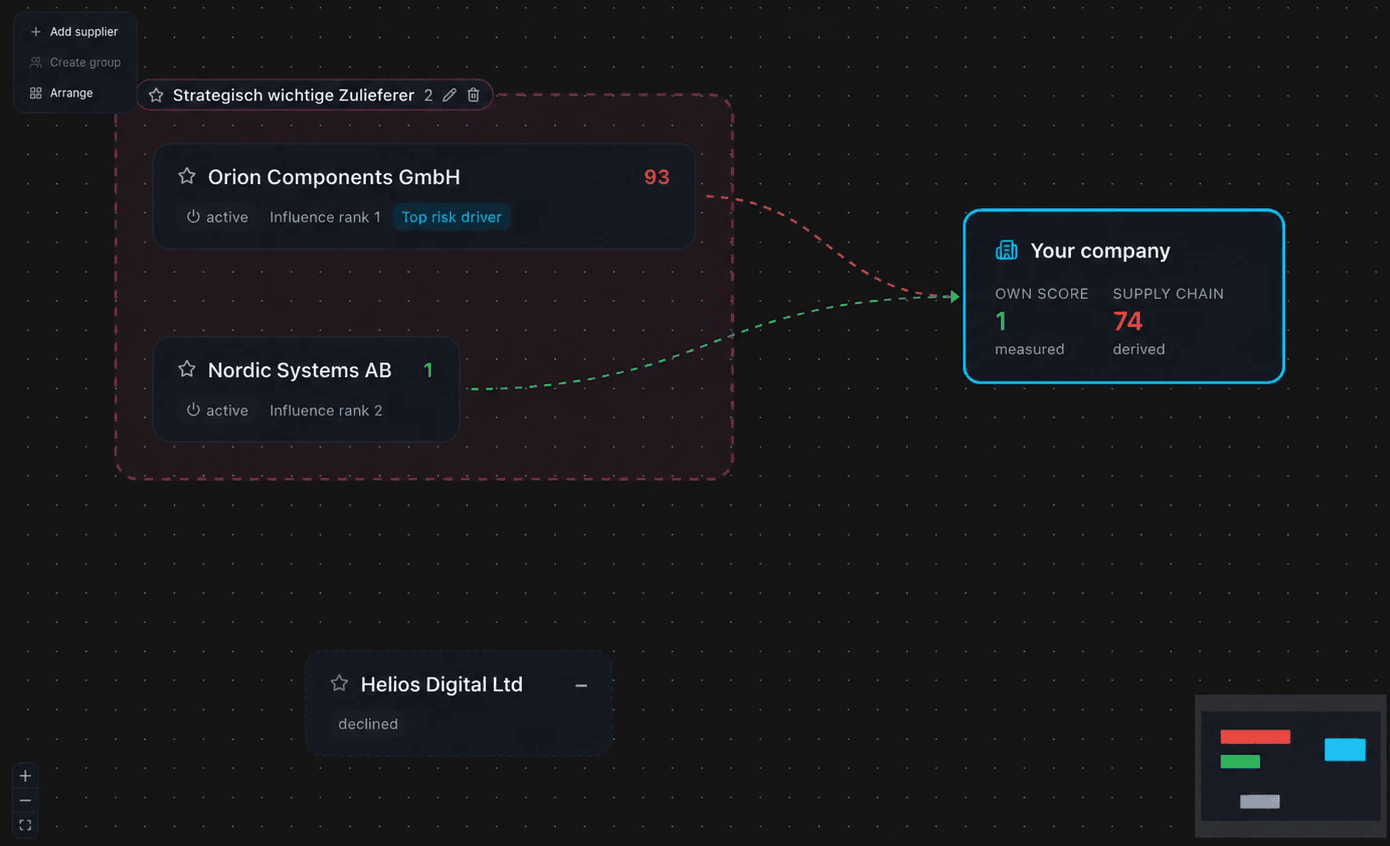
A cyber incident at a critical business partner can bring your own processes to a standstill – even if your own IT is excellently protected.
QSEIDON ATLAS combines the view of your external attack surface with the cyber risks of your suppliers and business partners.
Identify external risks, understand critical dependencies and prioritize action where it matters most to your business.
The challenge
Even if your own IT is excellently protected, cyber risks outside your organization can have a significant impact on your business processes.
Because your digital attack surface doesn’t end at your own systems.
External Attack Surface
Unknown IT assets, publicly reachable services, misconfigurations and undetected vulnerabilities can open up new opportunities for attackers.
Do you know what attackers can see of your organization?
Cyber Supply Chain Risk
Critical suppliers, external service providers and technology partners bring their own cyber risks. A security incident can impair their ability to deliver and, in turn, affect your business processes.
Do you know which cyber risks your critical suppliers bring with them?
Two risk dimensions. One connected view.
QSEIDON ATLAS combines the view of your external attack surface with an assessment of your supplier risks. This creates the foundation for better understanding cyber risks and business dependencies.
Cyber Creditworthiness
A business partner’s financial stability is an established decision criterion. But their cybersecurity can also be critical to the stability of your own business processes.
QSEIDON ATLAS applies the idea of a creditworthiness assessment to cyber risk – based on externally observable risk signals and taking business dependencies into account.
“How financially reliable is my business partner?”
Companies use financial information and credit ratings to better assess economic risks in business relationships.
An established decision criterion.
“What cyber risks does my business partner carry?”
ATLAS uses externally observable security signals to make an organization’s cyber risk posture easier to understand.
An additional perspective on business risk.
The idea: cyber risks should not only be visible to security experts, but also understandable and usable for business decisions.
ATLAS looks at externally observable risk signals, such as exposed services, known vulnerabilities and other indicators of the external security posture.
The observable risks form the basis for assessing an organization’s cyber risk posture in a structured and comprehensible way.
A supplier’s risk posture is viewed in the context of its importance to your organization and your dependencies on it. This makes it clearer which risks deserve particular attention.
Identifying cyber risks is the first step. Understanding what they mean for your business makes the difference.
ATLAS helps translate technical security signals into understandable, actionable information for business decisions.
The platform
QSEIDON ATLAS combines External Attack Surface Management with Cyber Supply Chain Risk Management. This keeps both your own external attack surface and the cyber risks of your suppliers and business partners in view.
Cyber Supply Chain Risk Management
Assess the externally observable cyber risks of your business partners and view them in relation to your business dependencies.
See which business partners deserve particular attention.
External Attack Surface Management
Identify your organization’s publicly visible systems, exposed services and known vulnerabilities, and prioritize the risks that matter.
Understand where your organization could be vulnerable from the outside.
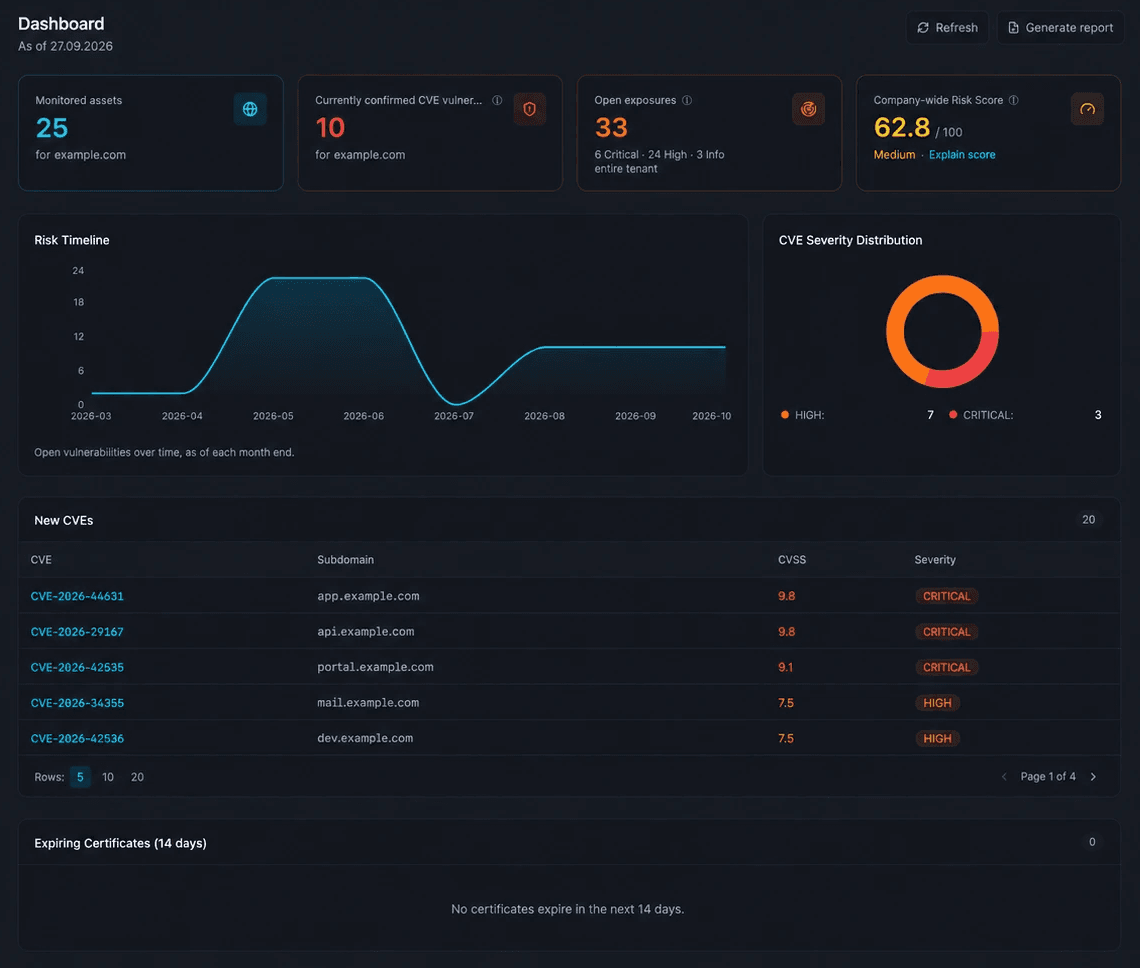
A shared view of external cyber risks – inside and outside your organization.
Business Impact
A cyberattack doesn’t have to target your organization to disrupt your business. When a critical supplier is affected, the consequences can reach your own operations.
A possible scenario
A critical supplier falls victim to a cyberattack.
Production or delivery is impaired – required components or services don’t arrive on time.
Your own production or other dependent business processes can slow down or come to a halt.
QSEIDON ATLAS helps you view your business partners’ cyber risks in the context of business dependencies and prioritize risks in a targeted way.
Continuous Visibility
Your cyber risk landscape is constantly changing – and so is that of your suppliers. New systems, vulnerabilities and supplier exposures can change your risk picture within a short time.
Today
A security assessment provides a risk picture for this point in time.
New cloud service
A new publicly reachable service expands the external attack surface.
New vulnerability
A newly disclosed vulnerability changes the risk assessment of a system.
New supplier exposure
New external risk signals become visible at a critical business partner.
Tomorrow
The original assessment may no longer fully reflect the changed risk landscape.
QSEIDON ATLAS helps organizations monitor changes in their external cyber exposure and supplier ecosystem, enabling risk-informed prioritization as conditions evolve.
Actionable Risk Intelligence
QSEIDON ATLAS helps you put technical cyber risks and business dependencies into context so you can set well-founded priorities. What matters is not only which risks exist, but which ones need attention first.
Result
Together, both perspectives show which risks, systems or suppliers deserve particular attention.
A traceable assessment instead of gut feeling. The assessment of external technical risks on your own attack surface takes into account, among other factors, severity (CVSS), exploit likelihood (EPSS), known exploits and the age of findings.
See which business partners deserve particular attention based on their externally observable cyber risk posture and your business dependencies.
Use external risk signals to prioritize the review and hardening of particularly relevant systems – for example as a basis for targeted penetration tests.
Translate technical risk information into clear decision support for executives, IT security, procurement and risk management.
Get started with QSEIDON ATLAS
Gain visibility into your external attack surface and your business partners’ cyber creditworthiness. Discover how QSEIDON ATLAS helps you understand critical risks and business dependencies and prioritize what matters most.
Explore the platform and its potential applications in a personal conversation.
EU Hosting
European hosting infrastructure.
Team Collaboration
Share risk insights across your team.
Personal Consultation
Explore ATLAS and its use cases together.
Interested in integrating ATLAS into your service portfolio? Let’s talk about a partnership.